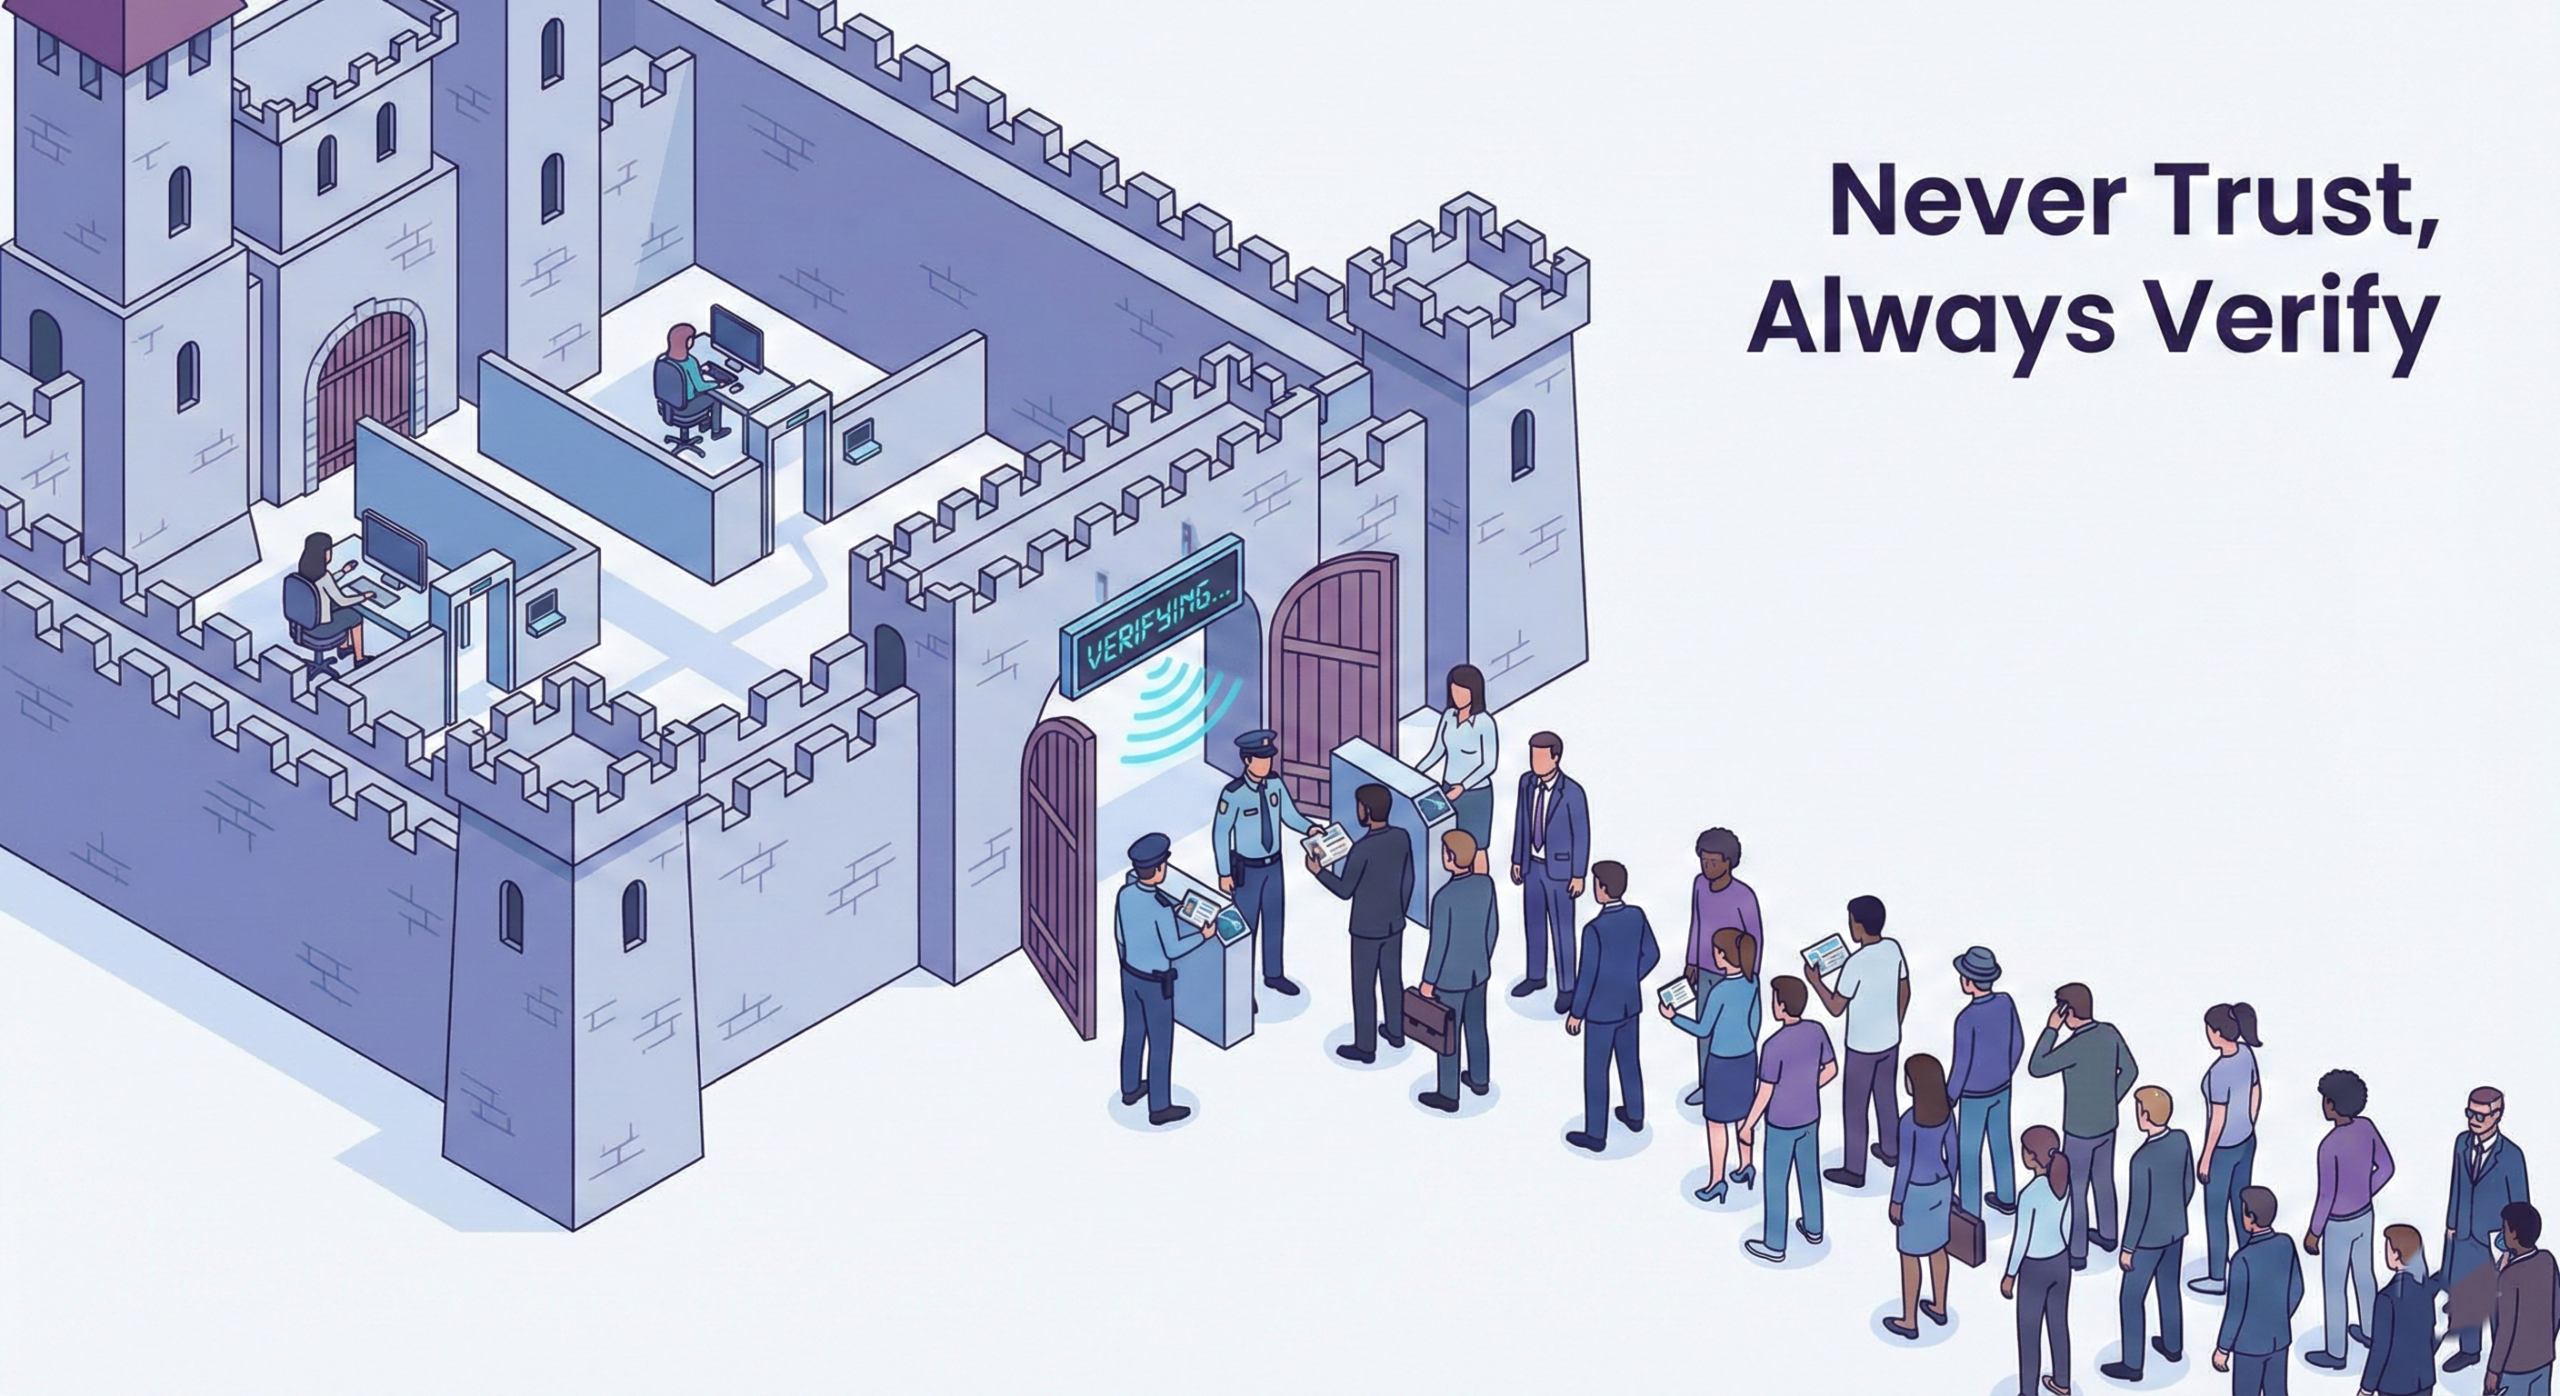
However, the threat posed by cyberattacks has never been as rampant as it is today, and the traditional security features are no longer warranted. Many organizations in the past have presumed that whatever is in their network can be trusted, but the contemporary reality is that it is not the case. It is an introductory resource to the zero-trust security framework that will educate you on how contemporary cybersecurity works and the reason as to why the adage of “never trust, always verify” is the new norm.
No matter whether you are a remote worker, a small business owner, or just a novice in the world of technology, the understanding of the concepts of Zero Trust may make you become much more digitally aware of your safety.
Defining Zero Trust Security Model.
Zero Trust Security Model This is a form of cybersecurity, where it is assumed that none of the users, devices, or systems should be trusted so long as they remain within the company network.
The identity and permissions are authenticated, in contrast to the choice to allow a person to gain access upon logging in.
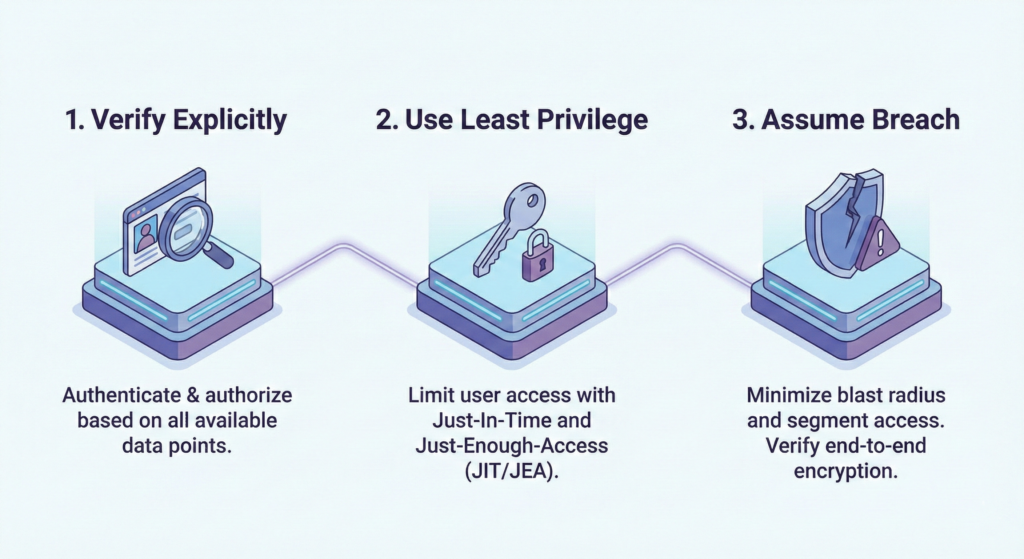
Significant Principles of Zero Trust Security.
Never trust by default
10. Check the identity and health of the device.
Restrict access to minimal privilege.
On-the-fly activity monitoring.
This method will reduce chances of information leaks as well as insider attacks.
The Cause of the Traditional Security Model Not Working Anymore.
The past security systems had their foundation on the idea of a strong perimeter, which is compared to a castle wall. Once inside, the users normally had broad access.
However, new places of work are not alike:
Remote work is common
Cloud apps are everywhere
The employees use personal devices.
There are more advanced cyberattacks.
Based on this, organizations need to be better enhanced in the protection aspect and this is where the Zero Trust architecture is needed.
The Zero Trust Security Model Operation.
Zero Trust is everything regarding admission and approval of requests in advance.
Identity Verification
Authentication of his identity: Any user must authenticate his identity:
Multi-factor authentication (MFA).
Biometric login
Secure passwords
Device Security Checks
The systems verify that:
The device is equipped with updated software.
Antivirus is enabled.
The operating system is safe.
Least Privilege Access
Only what is really needed by the users will be available.
For example:
Any marketing employee does not need to have access to financial systems.
A contractor can only grant access to one application.
Continuous Monitoring
Behavioral monitoring is conducted even after giving consent to determine abnormal behavior.
Zero Trust Benefits to Non-Technical Individuals and Businesses.
There are several advantages of a Zero Trust framework.
Stronger Data Protection
Minimizes damages caused by stolen credentials.
Reduces internal threats
Better Remote Work Security
Protects cloud applications and mobile devices.
Guarantees the remote working environment.
Improved Compliance
Helps are current as far as cybersecurity is concerned.
Provides details on the audit trail.
Simple Zero Trust Security How to Start with Zero Trust.
You do not have to have a huge IT division to begin to apply the ideas of Zero Trust. These are casual, newbie-friendly steps.
The initial procedure in the process is to do MFA.
This provides an extra layer of security in the case of passwords.
Action Plan 2: Use Formidable Access Control.
Role-based access control.
Step 3: Monitor Login Activity
Follow suspicious locations or devices with accounts.
Step 4: Secure Endpoints
Service laptops, smartphones, and tablets.
Step 5: Educate Users
Training of employees to detect phishing attacks augments the Zero Trust strategy.
Zero Trust Security Misconceptions.
Among the beginners, it is a common misconception that Zero Trust is complex or expensive, and this is not the case all the time.
Myth 1: Zero Trust is Zero Access.
Reality: It is only checking and allowing entry.
Myth 2: It Is Necessary in Large Companies Only.
Reality: Teleworkers and small enterprises make a fortune.
Myth 3: It Replaces All the Security Tools.
Reality: Zero Trust works together with firewalls, antivirus applications, and cloud security applications.
Best Practices when designing a Zero Trust Strategy.
To ensure your security model is effective, the following tips are feasible:
Implement secure identity management tools.
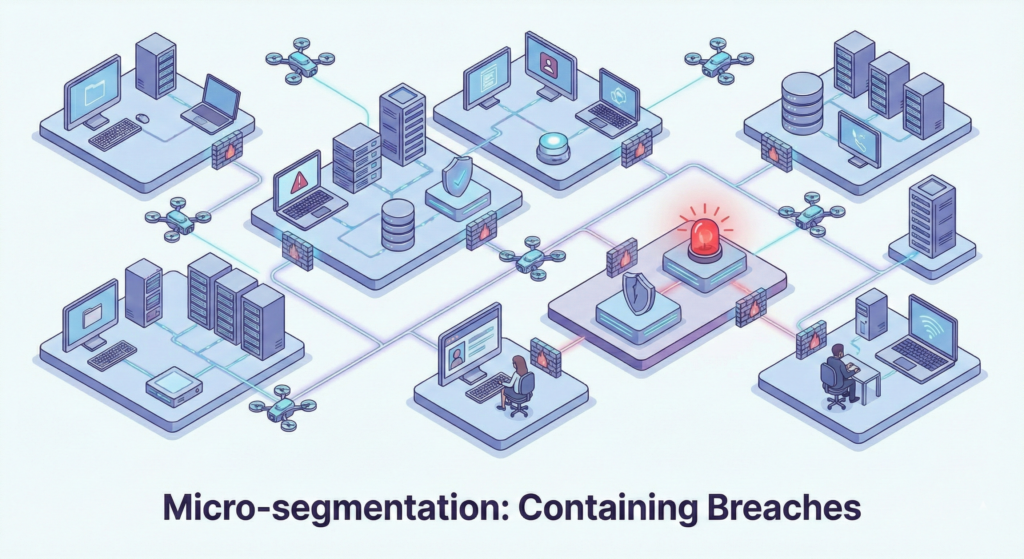
Breaking up networks should prevent movement between systems.
Cryptograph confidential information.
Periodical check access privileges.
Implement computerization of security alerts.
Such moves are a part of establishing a more effective posture on cybersecurity over the long term.
Conclusion
This beginner’s guide to the zero-trust security framework explains that in the modern world, cybersecurity is not about the walls, but it is about verification of all the attendances. By adhering to the principles of Zero Trust, like identity verification, least-privilege access, and round-the-clock monitoring, individuals and companies prevent the risks.
It is not technically intensive to start with. Even such basic actions as using multi-factor authentication, tending to the device, and tracing the movement will be capable of getting you one step closer to a safer Internet world.
Frequently asked question (FAQ)
Possibly in the simplest terms, what is Zero Trust?
Zero trust means that no one trusts a user or a device. Authorization in case of access should be verified after the verification of each access request.
Is Zero Trust security applicable only in large organizations?
No. Small businesses, freelancers, and remote workers can also be considered the users of the No. Zero Trust practices.
Is Zero Trust a replacement for firewalls or antivirus packages?
No. It has been utilized in conjunction with the existing tools in building a stronger layered security system.
Which is the ultimate advantage offered by Zero Trust architecture?
It reduces the chances of data breach because it makes sure that only the authorized users are allowed to access the data, and also the activity of the users is monitored.
How do novices start using Zero Trust?
Start with ensuring that you have multi-factor authentication, user permissions, updated devices, and frequently monitor user activity.