With all the chatter in the technology sector about quantum computing innovations and advanced artificial intelligence, in the real world of most start-ups, there exists something much more basic: the containerized applications. The Docker and Kubernetes technologies have completely changed the whole software creation, shipping, and scaling process. They help small teams to travel at a pace that is unbelievable.
You can think of security retrospectively when rushing to publish a minimum viable product (MVP). Eager teams also postpone it when implementing some new feature. Nevertheless, a single malfunctioning configured container will expose your business to disastrous data breaches.
You are at the correct space and location in the event that you desire to envelop your cloud-native infrastructure without reducing your growth or development cycles. We are going to dive into the most applicable container security best practices among startups.

The explanation of why container security is crucial to startups.
Start-ups operate in a high-stakes environment. You must operate with a limited budget, tight deadlines, and the need to be innovative at any given time. Why do you have to bother about container security now?
Protect Customer Trust: A data security breach will destroy a new business within a few hours.
Compliance Requirements: When sensitive data are at stake, such frameworks as SOC 2, HIPAA, or GDPR require a high level of security.
Economic Impact: It would be costly to react to a cyberattack. Most of the startups also cannot afford the downtime and the legal expenses incurred in case of breach.
Compound Surfaces of Attack: Containers are movable. They spin vertically and horizontally continuously, making the traditional perimeter security technologies useless.
There is an opportunity to establish a robust security posture that can expand in line with your business with a DevSecOps approach.
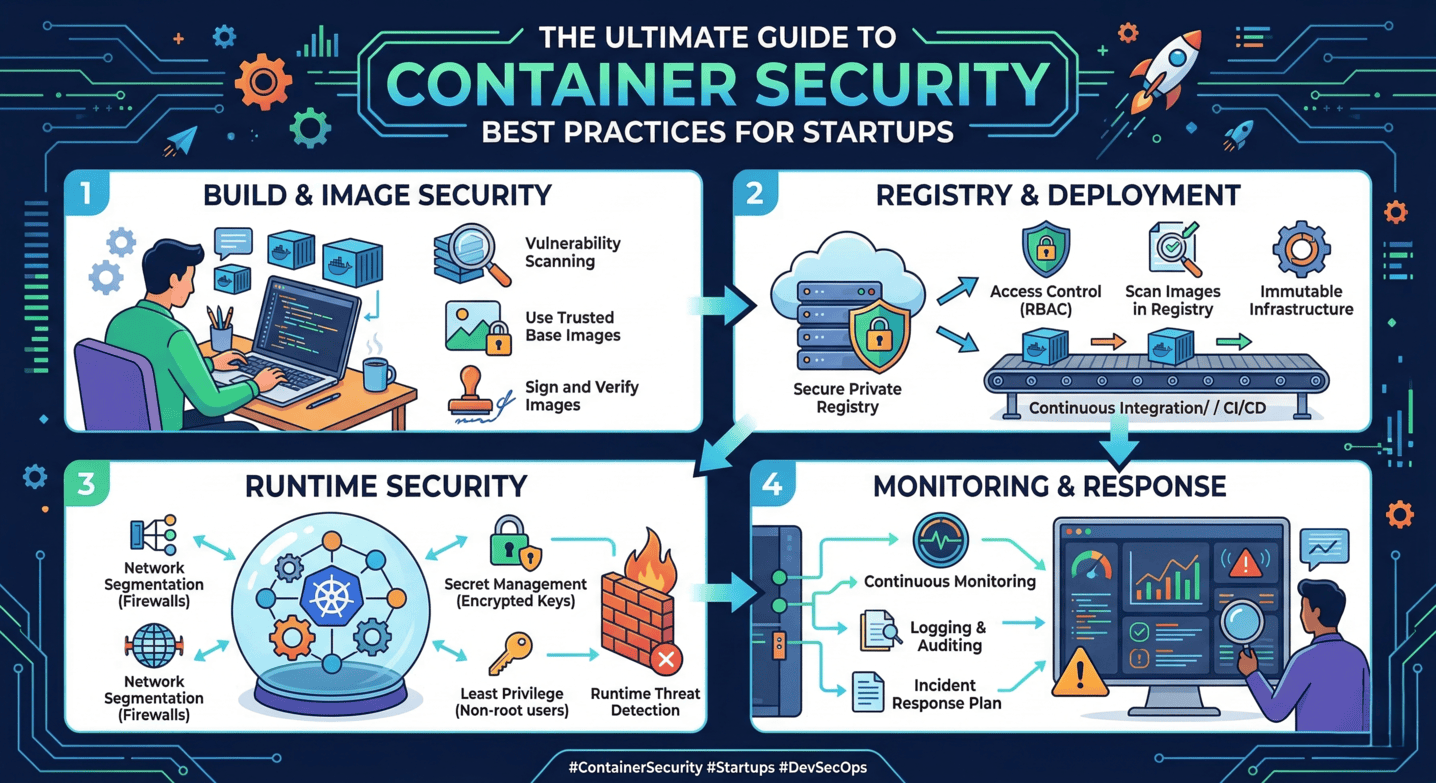
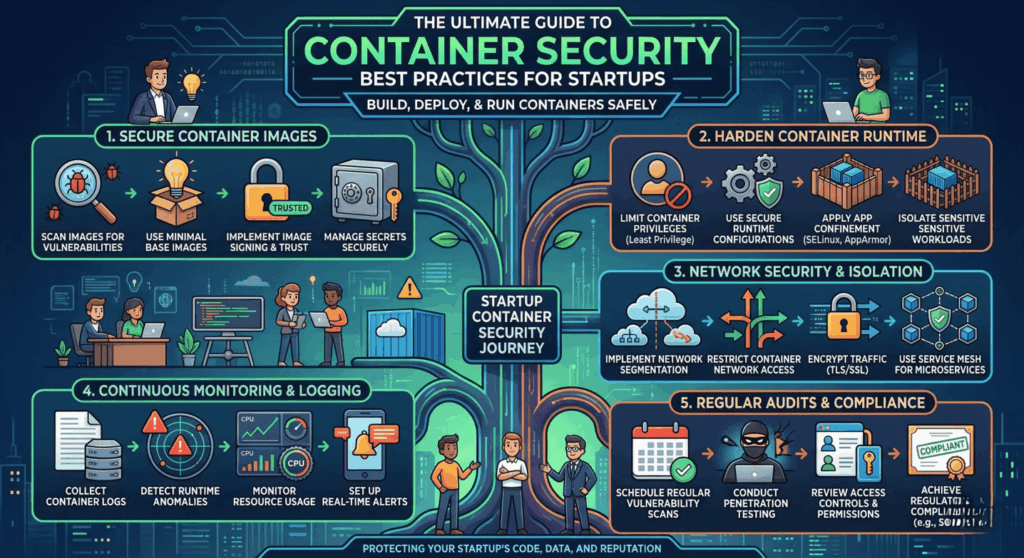
Minimal and Trusted Base Images.
A container starts from its base picture. Your base image may be bloated or contain holes even before it has started up, and it is subject to attack.
Pull images only from official repositories, like those of official publishers in Docker Hub, and treat them as trusted.
Limit images: How to work with distressed images or lightweight OSs, like Alpine Linux. The fewer intruders there are in the less equipment and libraries in the container, therefore the smaller the area of attack.
Do not use the current tag. You are always supposed to attach your pictures to a specific version (e.g., node:18.17.1-alpine). This serves as an aid to preventing gotchas by leaving new vulnerabilities in a surprise update as well as making your builds reproducible.
Continue to scan the registries. From today to tomorrow, an image can look safe, but researchers may discover a new vulnerability. Compare your container registries with published new threats periodically.
Adopt the Least Privilege Principle.
Grant them only the permission to run containers, which is essential. Excess privileges are the most prevalent cause of container breakage.
Do not execute as root. Most containers execute as root by default. Fix this by altering this to a non-root user in your Docker file.
Cut down capabilities that are not required: Disable Linux kernel capabilities unnecessary to your application.
Use RBAC. Role-Based Access Control (RBAC) is a Kubernetes resource management application. It then lets you limit access to your container orchestration system by users and/or prohibited resources.
Manage Secrets Securely
It is a time bomb to embed your API keys, database passwords, or authentication tokens in your image. It can also destroy your infrastructure in case your image is ever leaked out.
Keep sensitive data in the environment variables. Only as an environment variable can you easily disclose sensitive data in the crash report or the logs.
Use secrets manager: Inject sensitive data into your containers: HashCorp Vault, AWS Secrets Manager, or Kubernetes Secrets can inject sensitive data into your containers.
Container Runtime Behavior Monitoring.
This is highly required, but you should also know whether an attacker can make it through the loopholes. Runtime security has got interest in what happens after deployment of your container.
Check network traffic: Earlin monitors the suspicious communication patterns, e.g., a frontend container, which simultaneously tries to communicate to an external, unknown IP address.
Isolate container networks: Network policies restrict the inter-pod traffic. Only allow containers, for example, to communicate when they know they need to communicate.
Use threat detection: You can use runtime security tools to detect suspicious behavior, such as unexpected file modifications or unwanted execution of processes, e.g., Falco.
Secure Your CI/CD Pipeline
Your Continuous Integration and Continuous Deployment (CI/CD) pipeline is the gateway to your world of production. Should some hacker intrude into your pipeline, he has control of your application.
Restricting access: Allowed access to code pushes and deployments.
Sign your images with a cryptographic signature (i.e., Cosign). This ensures that the image you deploy is the same image that passed your checks in the pipeline.
Building an operation culture based on descopes.
Half of the battle is merely with means and settings. Full container security requires your change of company culture.
Train your programmers about safe programming and make measures of security visible to all the team members. Then treat security bugs just like any software bug. When you have turned the security collective, your startup will be much harder to break.
Conclusion
The most successful container security best practices for start-ups are not about building an impenetrable fort on the first day. It is as well concerning making smart, mini, gradual modifications of risk decrease, which are radical. Having a small number of images, automated vulnerability checks, least privilege, and leveraging the power to be able to observe what you are running, you will be able to protect your startup data and scale it without hesitation. Start chipping in these steps today and therefore inculcate security into the DNAs of your company.